Controls that keep working
A firewall rule, a login lockout or a scheduled scan does its job whether or not anyone is watching. What a person reviews, and how often, is agreed in the scope.
Cyber security services
We assess, harden and monitor public-facing applications, APIs, cloud services and sensitive data paths with clear scope and practical response.
Businesses we have worked with
Firewall, bot, DDoS, DNS, CDN and cloud platform protection for the systems on your public path.
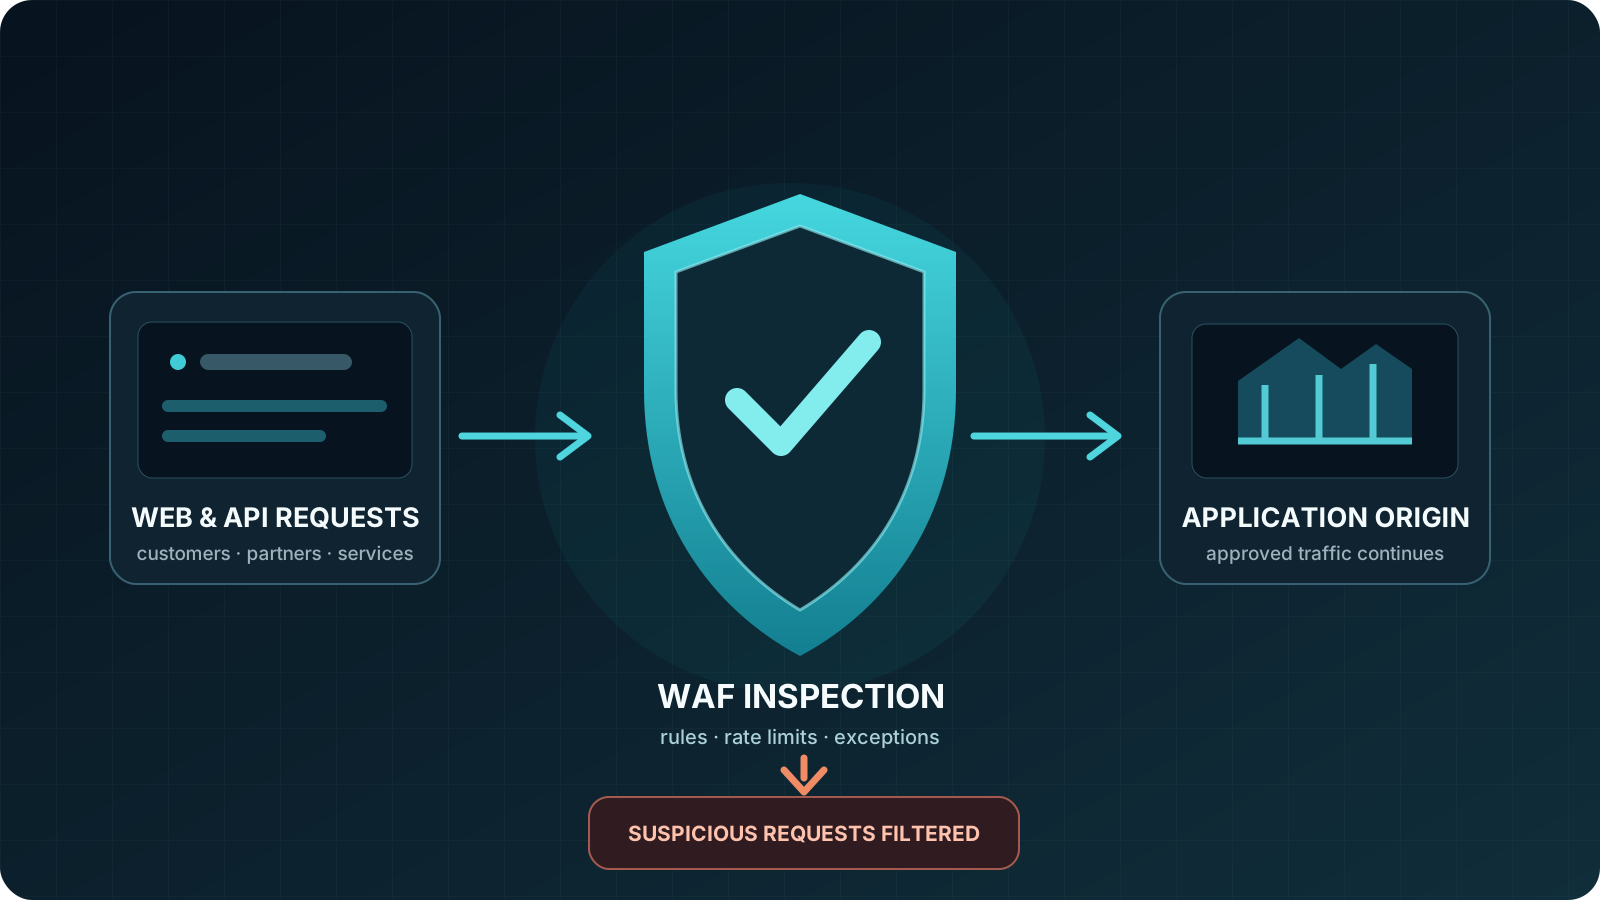 Web Application Firewall
Deploy and tune a WAF to filter malicious HTTP traffic while keeping legitimate customers, integrations and business-critical journeys moving.
Learn more
 Bot Protection
Reduce scraping, fake signups, credential stuffing and automated abuse without blocking search engines, partners or legitimate customers.
Learn more
 DDoS Protection
Plan mitigation, routing and response so your websites, APIs and network services stay reachable while an attack is in progress.
Learn more
 DNS Protection
Review the domains, records, accounts and providers your websites, applications and email depend on, before a change or an outage takes them offline.
Learn more
 Account Takeover Protection
Review login, multi-factor, session and recovery journeys so a stolen password on its own is less likely to open a customer account.
Learn more
 Content Delivery Network
Plan caching, origin protection and edge configuration around how your application actually serves customers.
Learn more
 AI Application Security
Review the data, permissions and tool access behind your AI features so they stay useful without becoming a new way into your systems.
Learn more
 AWS Application Security
Review identity, storage, network exposure, secrets and logging against the way your application is actually built and operated.
Learn more
 Google Cloud Application Security
Review workloads, service accounts, storage exposure, network ingress and audit logging against the way your application actually runs.
Learn more
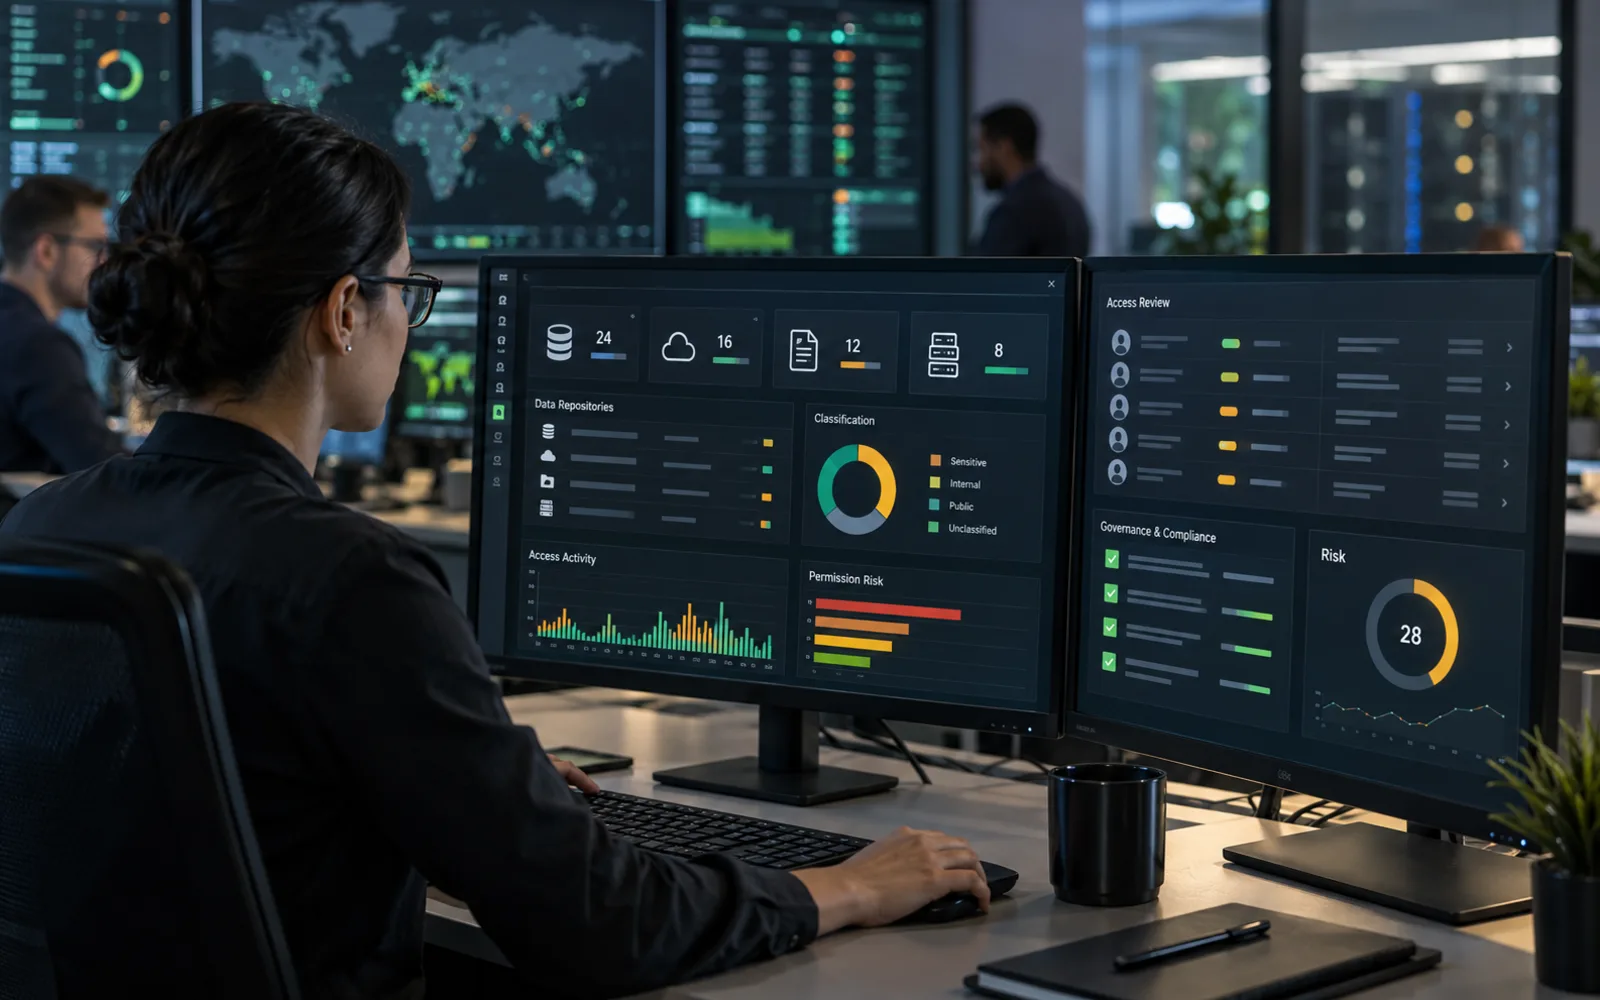
Connect discovery, classification, posture management, monitoring, analytics, governance and cloud data protection into one practical service scope.
Identify the databases, cloud stores, SaaS systems, applications and owners involved in the requested data security scope.
Review how sensitive data can be reached, shared, misconfigured or overexposed across platforms.
Define ownership, reporting, remediation and evidence expectations so data security work becomes usable after the initial review.
Store, application, server and company device security reviews for the platforms you already run.
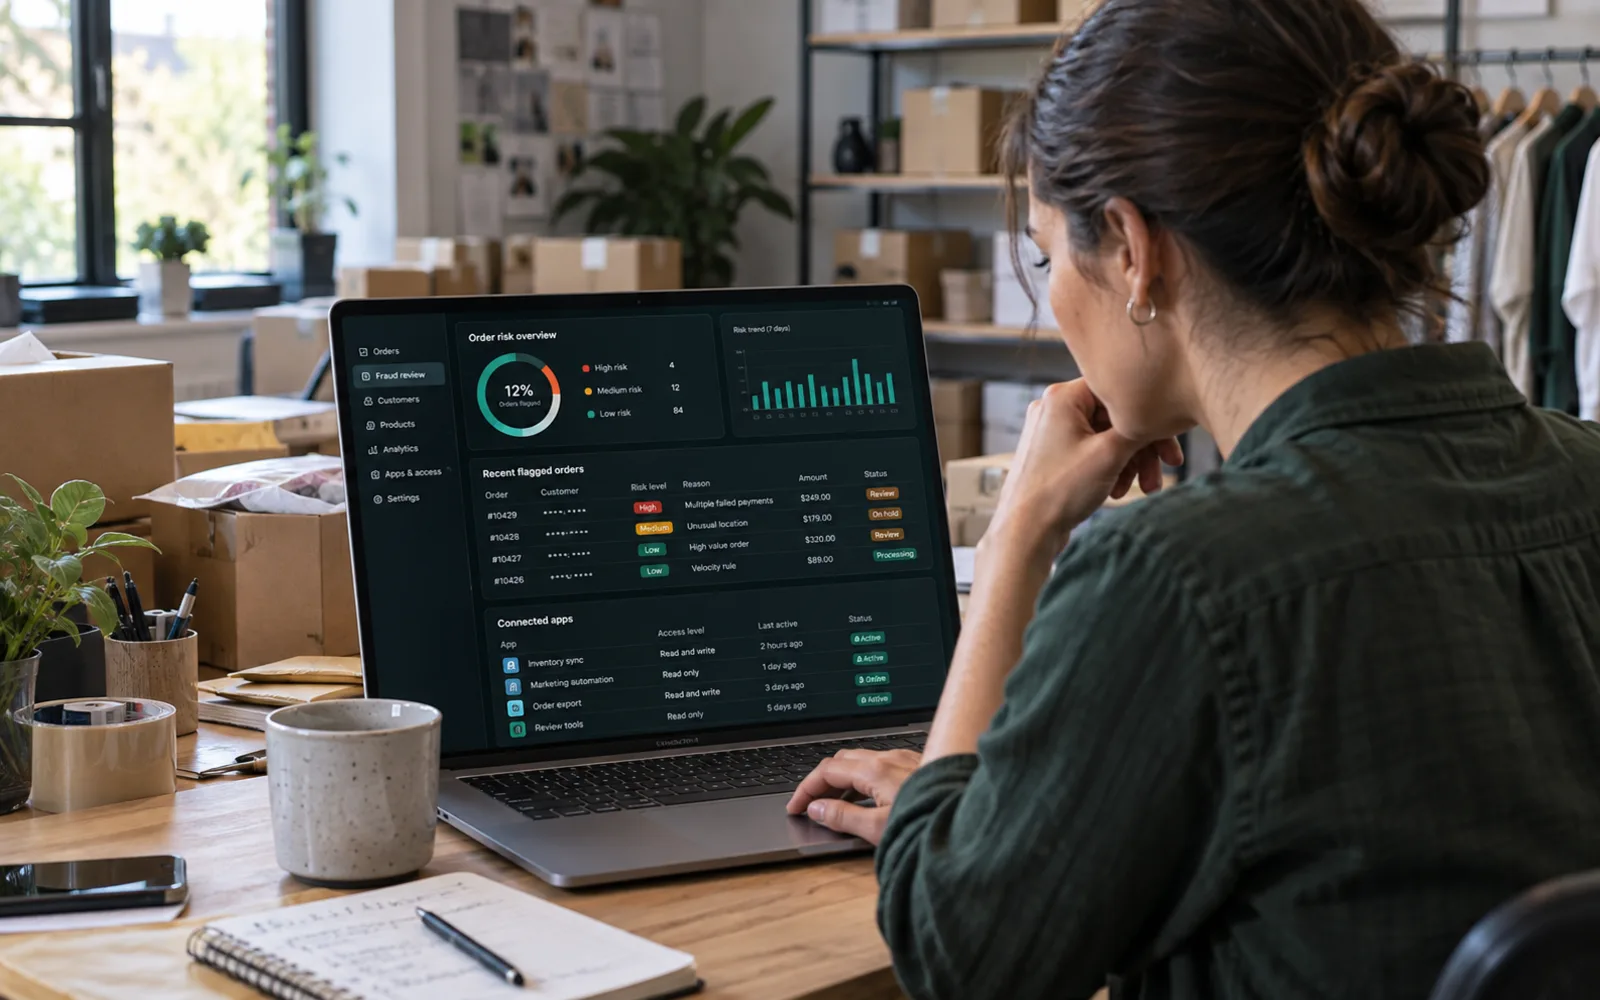 Shopify security
Get help with spam orders, suspicious activity and the security settings that matter to your Shopify store.
Learn more
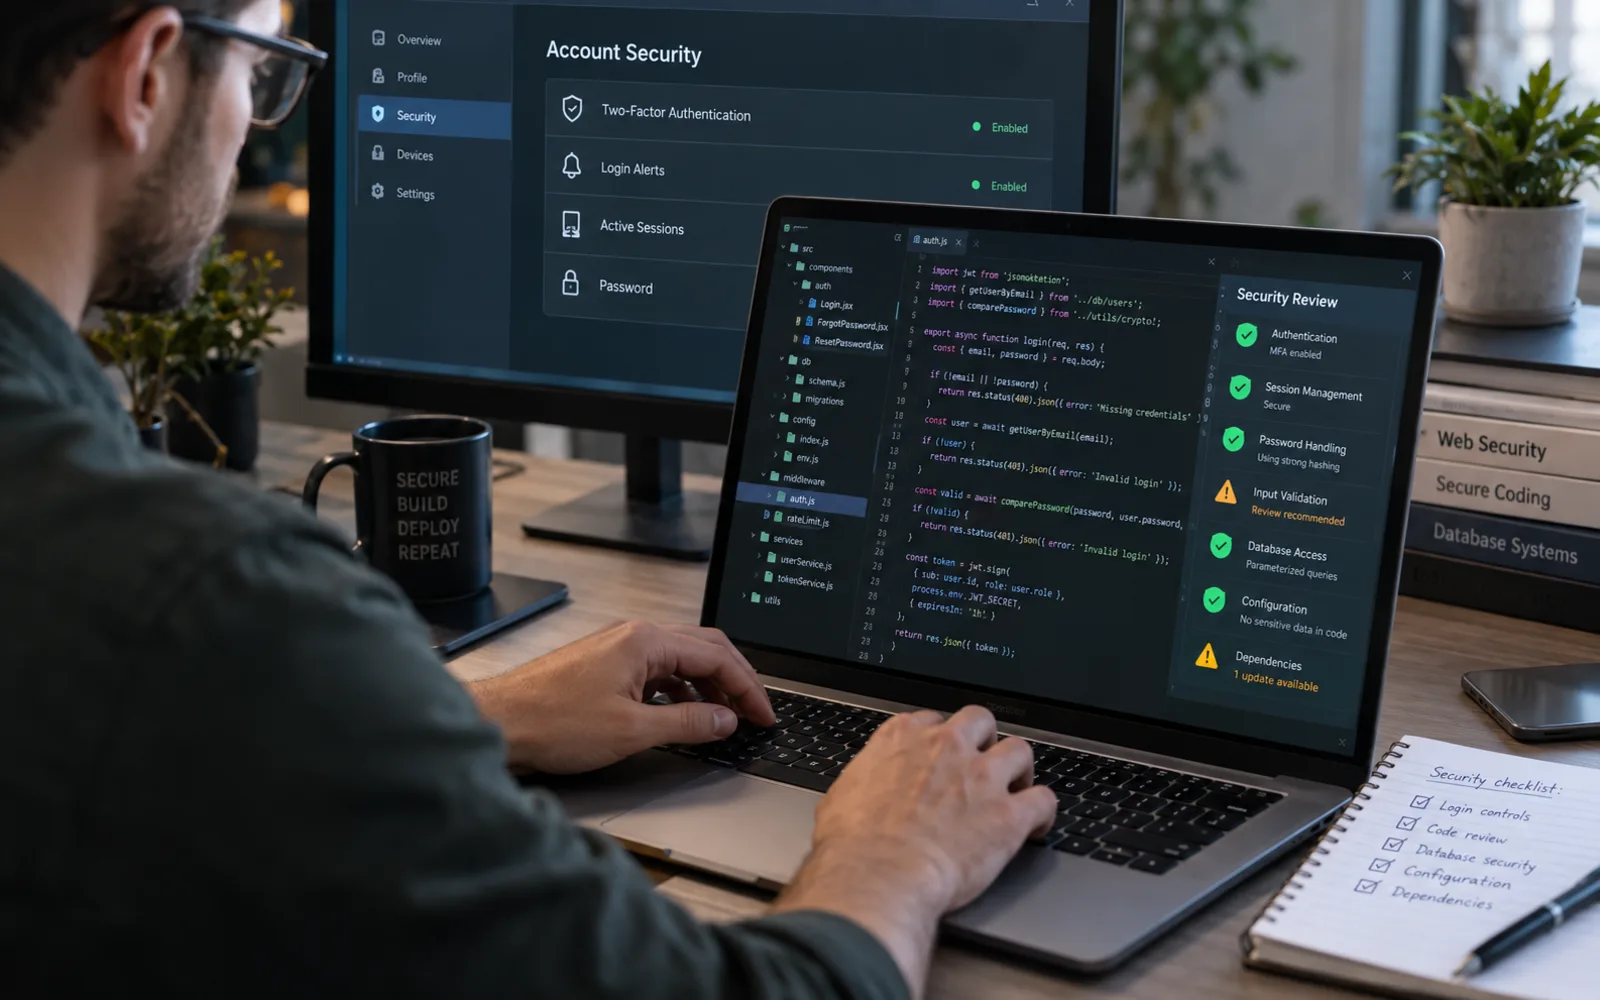 Website security
Practical reviews of login controls, database access and website settings for Laravel and custom websites.
Learn more
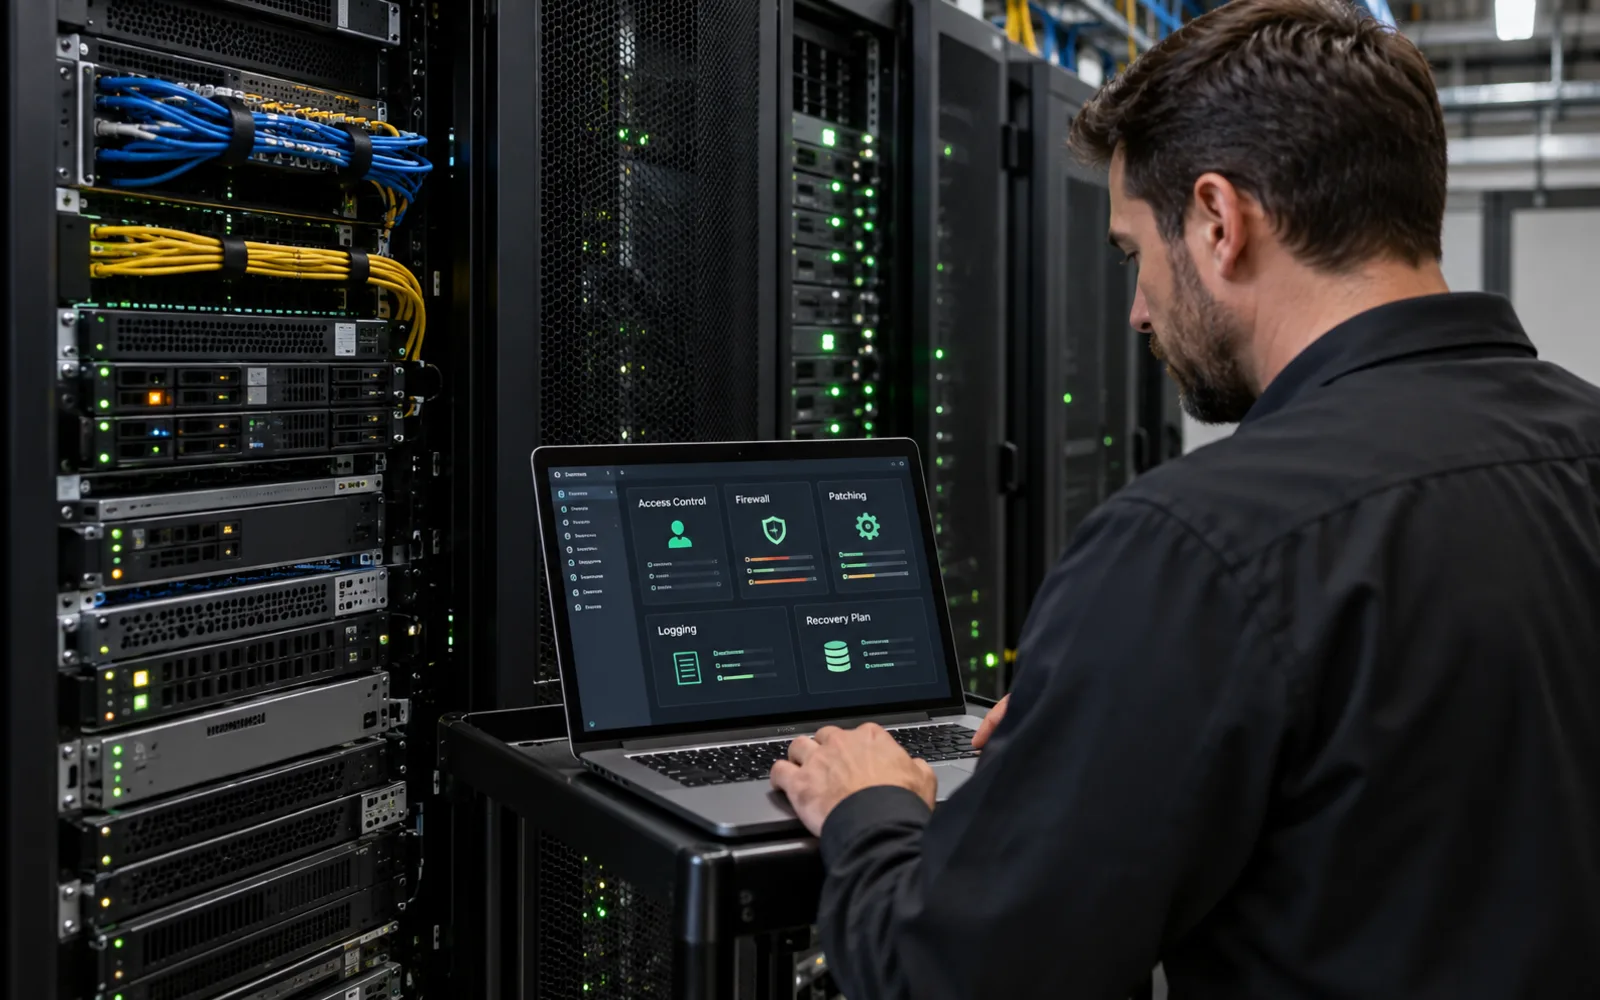 Server security
Understand exposed services, tighten access and plan the next steps for a more secure server.
Learn more
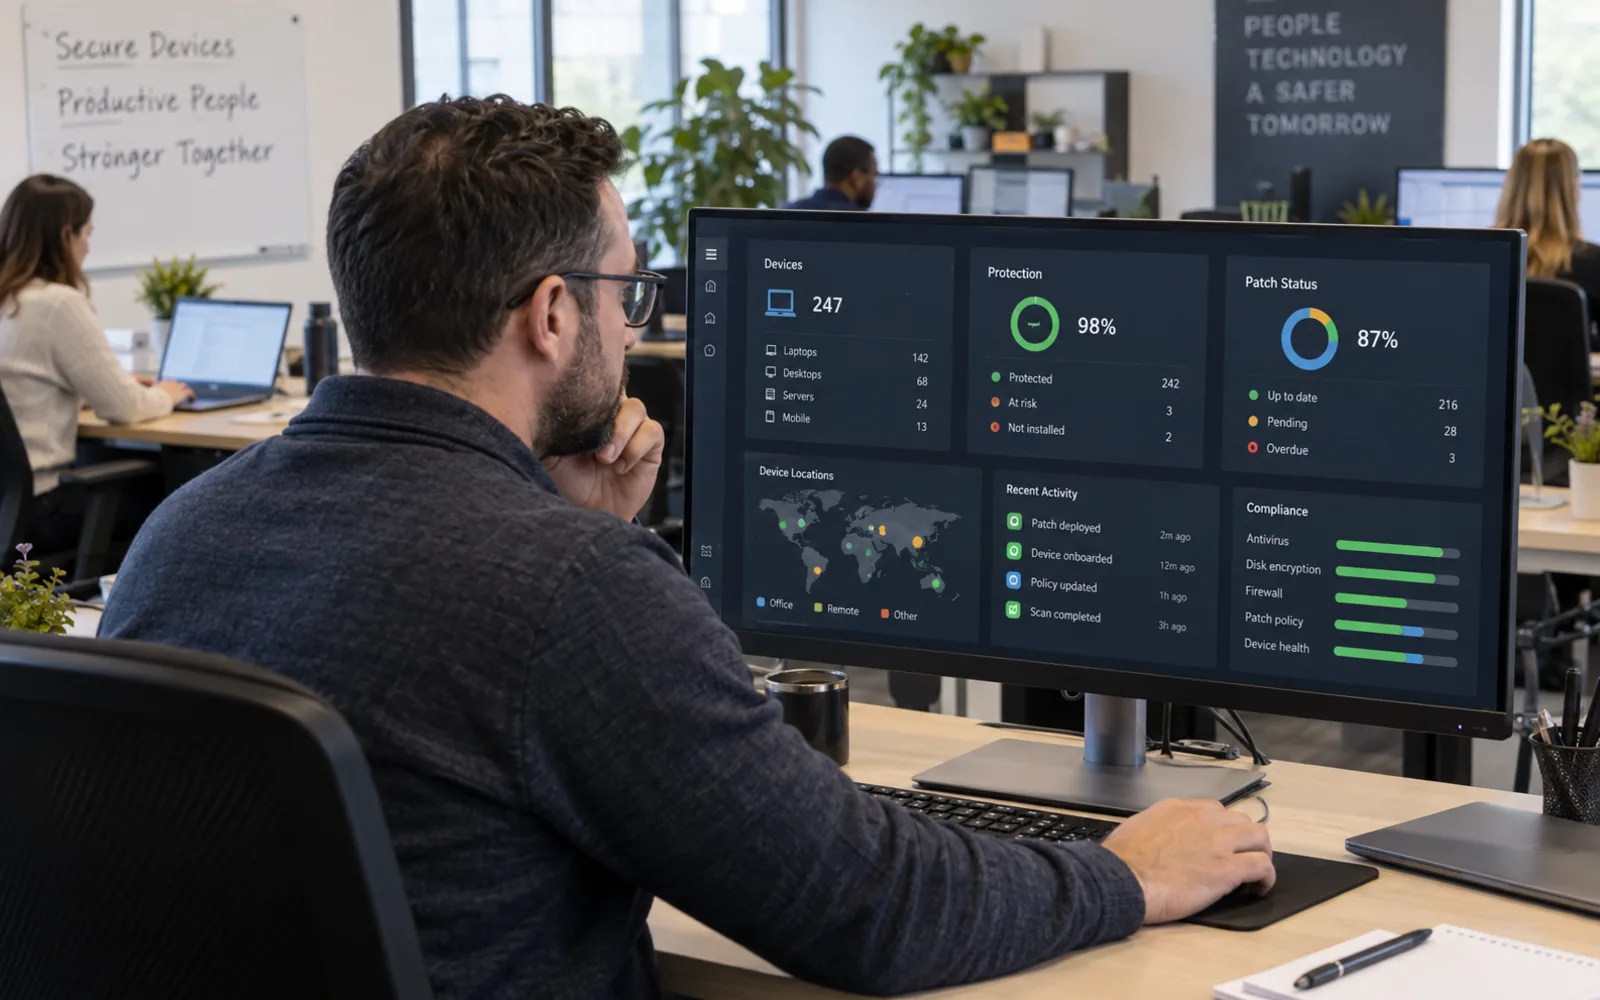 Company device security
A clear device inventory, practical security recommendations and a scope that follows your actual device list.
Learn more
Independent assessment, tooling integration and recurring managed support.
 Security Integration
Design integrations so the signals that matter reach an owner who can act, with enough context to make a decision.
Learn more
 Managed Security Services
Define a recurring service around the systems, controls and response responsibilities your business actually needs.
Learn more
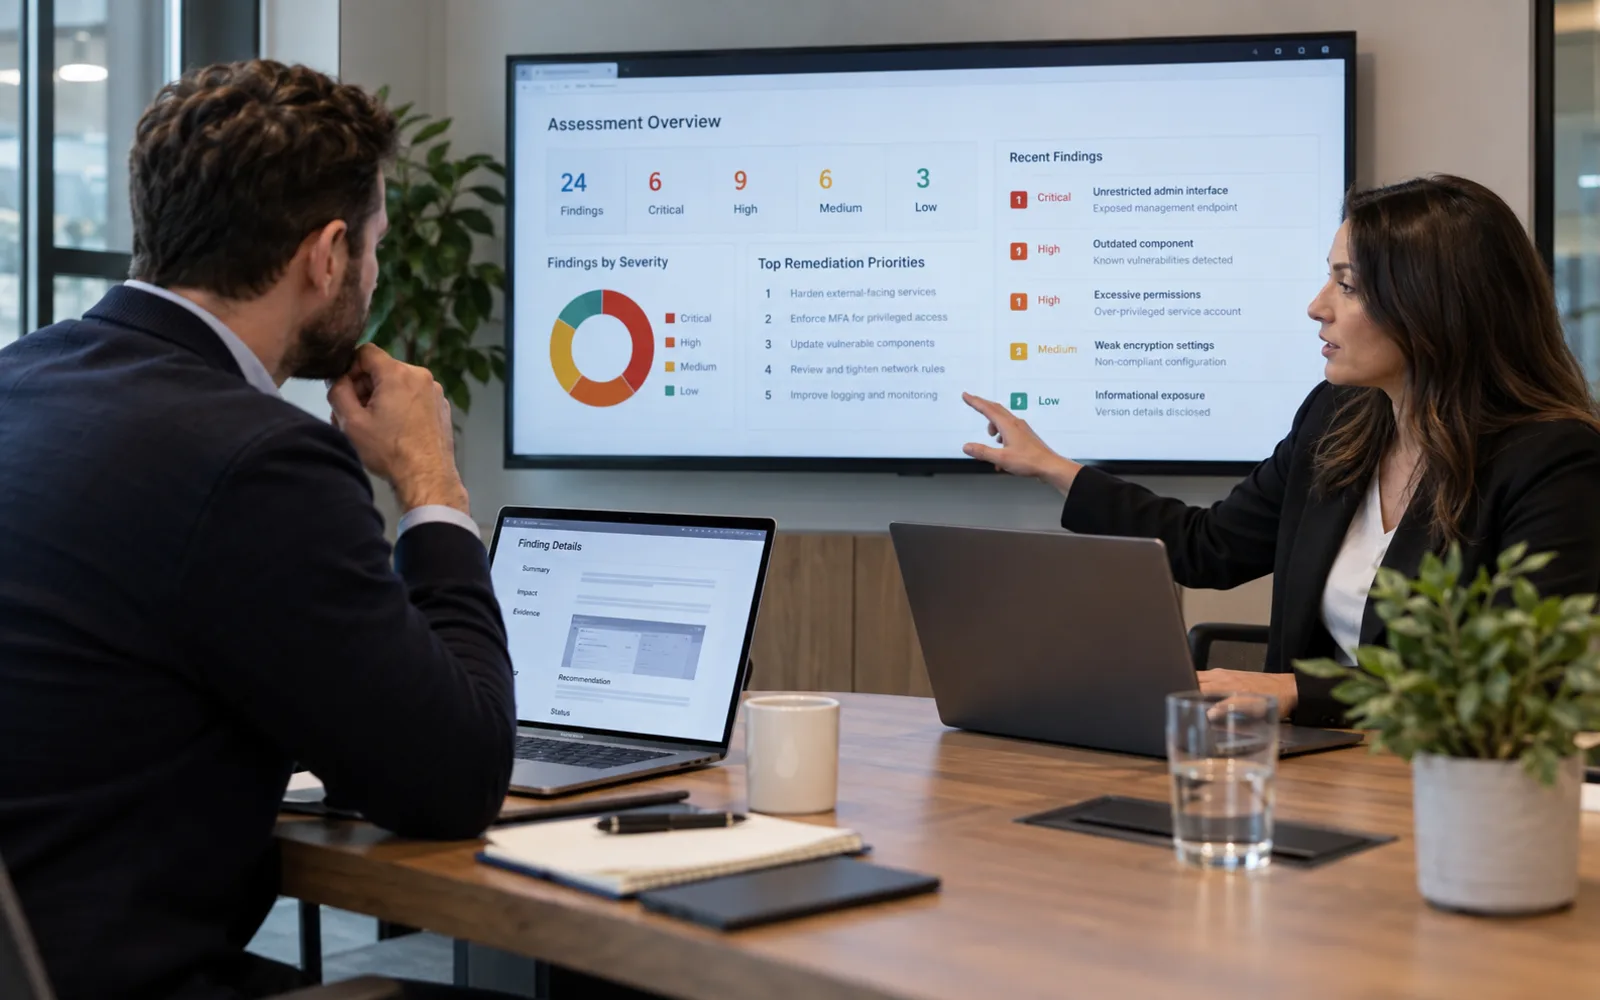 Security Assessment
Scope an assessment that answers a specific question about your applications, infrastructure or data, and ends in prioritised actions.
Learn more

W3Techs measures WordPress at 40.1% of all websites (October 2026), which makes it a constant target for automated attacks. MaxMindSecurity Pro, our WordPress plugin, adds a firewall, login protection, scanning and an audit log inside the site, licensed and managed from its own dashboard.
The scanner compares WordPress core files with the official checksums, checks plugins, themes and uploads for backdoors and web shells, and flags outdated or withdrawn plugins.
Repeated failed sign-ins lock the address out, the login page can sit at a custom address behind reCAPTCHA, and two-factor authentication makes a stolen password useless on its own.
Requests carrying SQL injection, cross-site scripting or path traversal patterns are blocked inside WordPress before a plugin or the database handles them, and every block is logged.
If a site is already compromised, clean-up is a separately scoped and quoted service: investigate, remove what access allows, restore safer files and harden afterwards.
No generic bundles and no forced migrations. The work is shaped around your hosting, your cloud platform and the tools your team already knows.
Hands-on security work on public websites, the applications behind them and the cloud accounts they run in, from single WordPress sites to larger estates.
Every engagement is scoped around your hosting, cloud platform and existing tooling. No generic bundle, no forced migration.
Incident response, malware removal and recurring monitoring are scoped and quoted like any other service, so you know in advance what is covered, when work happens and who to contact.
The first conversation is about what you run and what is worrying you. The service, the scope and the price follow from that, and all three are confirmed in writing before anything begins.
We review what you run, how traffic and data reach it, the controls in place today and the concern behind the request.
We agree the systems, the method, the deliverables, the responsibilities on each side and the commercial terms in writing.
We carry out the agreed work with clear updates, raising anything urgent as soon as it is found rather than saving it for a report.
You are left with prioritised findings, documented decisions and a named owner for each next step.
Security spending is easier to justify once you can see what an incident costs. Google can show a warning label in search results for a hacked or malware-hosting site, a tampered checkout stops orders, and a rebuild takes longer than prevention. Our guide to firewalls, malware scanners and backups explains which layer covers which risk.
A firewall rule, a login lockout or a scheduled scan does its job whether or not anyone is watching. What a person reviews, and how often, is agreed in the scope.
Incident reports are picked up ahead of other enquiries, so containment and clean-up start sooner.
Google checks sites for malware and can label an infected one in search results and in the browser. Keeping malware off your site protects the traffic you have earned.
An outage or a tampered checkout stops orders. Protection at the edge and on the server reduces how often that happens and how long it lasts.
Show visitors and partners their data is looked after by people who do this every day.
Protection lowers the odds of a compromise but does not remove them. A backup you have actually restored is what gets the site back when something gets through.
How services are chosen, how quotes are put together and what happens once work starts.
You do not have to decide before getting in touch. Most enquiries start with a symptom rather than a service name: unusual traffic, a failed customer security review, an upcoming launch, or a cloud environment nobody has examined in a while. Describe the situation and we will confirm which service fits, or tell you if none does.
Usually, yes. Services are scoped around your existing hosting, CDN, DNS, cloud platform, identity provider and security tooling. Share what you hold, including licence tiers, and we will confirm what is supported before proposing anything.
Every engagement is quoted after the requirements are reviewed. Scope, technology, effort, support hours and responsibilities are confirmed in a written proposal, so the price reflects the actual work. There is no charge for the initial conversation.
Both. Many engagements are a scoped piece of work such as an assessment, a firewall rollout or a cloud review. Where recurring attention is needed, a managed arrangement defines what is covered, how often it is reviewed and how escalation works.
It should not, and you can check. A firewall or CDN in front of the site adds a small processing step to each request, and caching at the edge usually gives that time back. If page speed matters to you, say so when work is scoped: measuring response times and Core Web Vitals before and after a change, and tuning rules that cost time, then becomes part of the deliverables.
Protection lowers the chance of a compromise; it does not remove it, and no provider can promise otherwise. If a site we look after is compromised, tell us straight away. We confirm what your agreed scope covers: where incident response or malware removal is included, that work starts at once; where it is not, we quote it as a separate piece of work and give you the cost before starting. Our guide to hacked website warning signs explains what to preserve and what not to touch in the meantime.
We review the enquiry and come back to discuss scope. Nothing is deployed, tested or changed until scope, authorisation and commercial terms are agreed in writing. Please do not send passwords, access keys or customer data with an initial enquiry.
Have a different question? See all frequently asked questions
Share the website, application, API, cloud environment or data concern behind the request. We review it and come back with a practical next step and a scoped proposal.
Prefer email? Write to care@maxmindsecurity.com or use the contact page.
We will review what you sent and reply to your email address. Nothing starts until scope and price are agreed in writing.
Explore services in the meantime