Skip to content
Request a quote
MaxMindSecurity services

Security services for the systems your business runs on.

Application, cloud, data, platform and managed security work, scoped around what you already run. Start with the concern rather than the package, and we will shape the right engagement around it.

Web, API and cloud

Application security

Protect the public websites, APIs, cloud workloads and delivery paths your customers, partners and staff use every day.

Web Application Firewall

Deploy and tune a WAF to filter malicious HTTP traffic while keeping legitimate customers, integrations and business-critical journeys moving.

  • WAF architecture and origin protection
  • Managed rules and application-specific policy
  • Logging, testing and safe rollout
Bot Protection

Reduce scraping, fake signups, credential stuffing and automated abuse without blocking search engines, partners or legitimate customers.

  • Bot traffic and abuse journey review
  • Detection signals and response planning
  • Customer-safe rollout and exceptions

DDoS Protection

Plan mitigation, routing and response so your websites, APIs and network services stay reachable while an attack is in progress.

  • Exposure and traffic-path review
  • Mitigation design and provider fit
  • Detection, activation and response

DNS Protection

Review the domains, records, accounts and providers your websites, applications and email depend on, before a change or an outage takes them offline.

  • Domain, zone and record inventory
  • Registrar, provider and account security
  • Resilience, monitoring and recovery

Account Takeover Protection

Review login, multi-factor, session and recovery journeys so a stolen password on its own is less likely to open a customer account.

  • Authentication entry points and credential abuse
  • Session handling and sensitive actions
  • Recovery, support and response

Content Delivery Network

Plan caching, origin protection and edge configuration around how your application actually serves customers.

  • Cache policy and content classification
  • Origin protection, TLS and routing
  • Invalidation, testing and operations

AI Application Security

Review the data, permissions and tool access behind your AI features so they stay useful without becoming a new way into your systems.

  • Input handling and prompt injection
  • Data access, retrieval and identity
  • Tool permissions and output handling

AWS Application Security

Review identity, storage, network exposure, secrets and logging against the way your application is actually built and operated.

  • Identity, roles and permission boundaries
  • Storage, network exposure and secrets
  • Logging, deployment and change ownership

Google Cloud Application Security

Review workloads, service accounts, storage exposure, network ingress and audit logging against the way your application actually runs.

  • Service accounts and IAM inheritance
  • Storage, data services and network ingress
  • Secrets, logging and deployment control
Sensitive data

Data security

Understand what sensitive data you hold, where it lives and who can reach it across databases, cloud storage and business systems.

Data Security

Connect discovery, classification, posture management, monitoring, analytics, governance and cloud data protection into one practical service scope.

  • Data landscape
  • Access and exposure
  • Operating model
Stores, servers and devices

Platform and endpoint

Reviews for the platforms a business already runs on: an ecommerce store, a custom application, a server, or the computers your team works from.

Shopify security

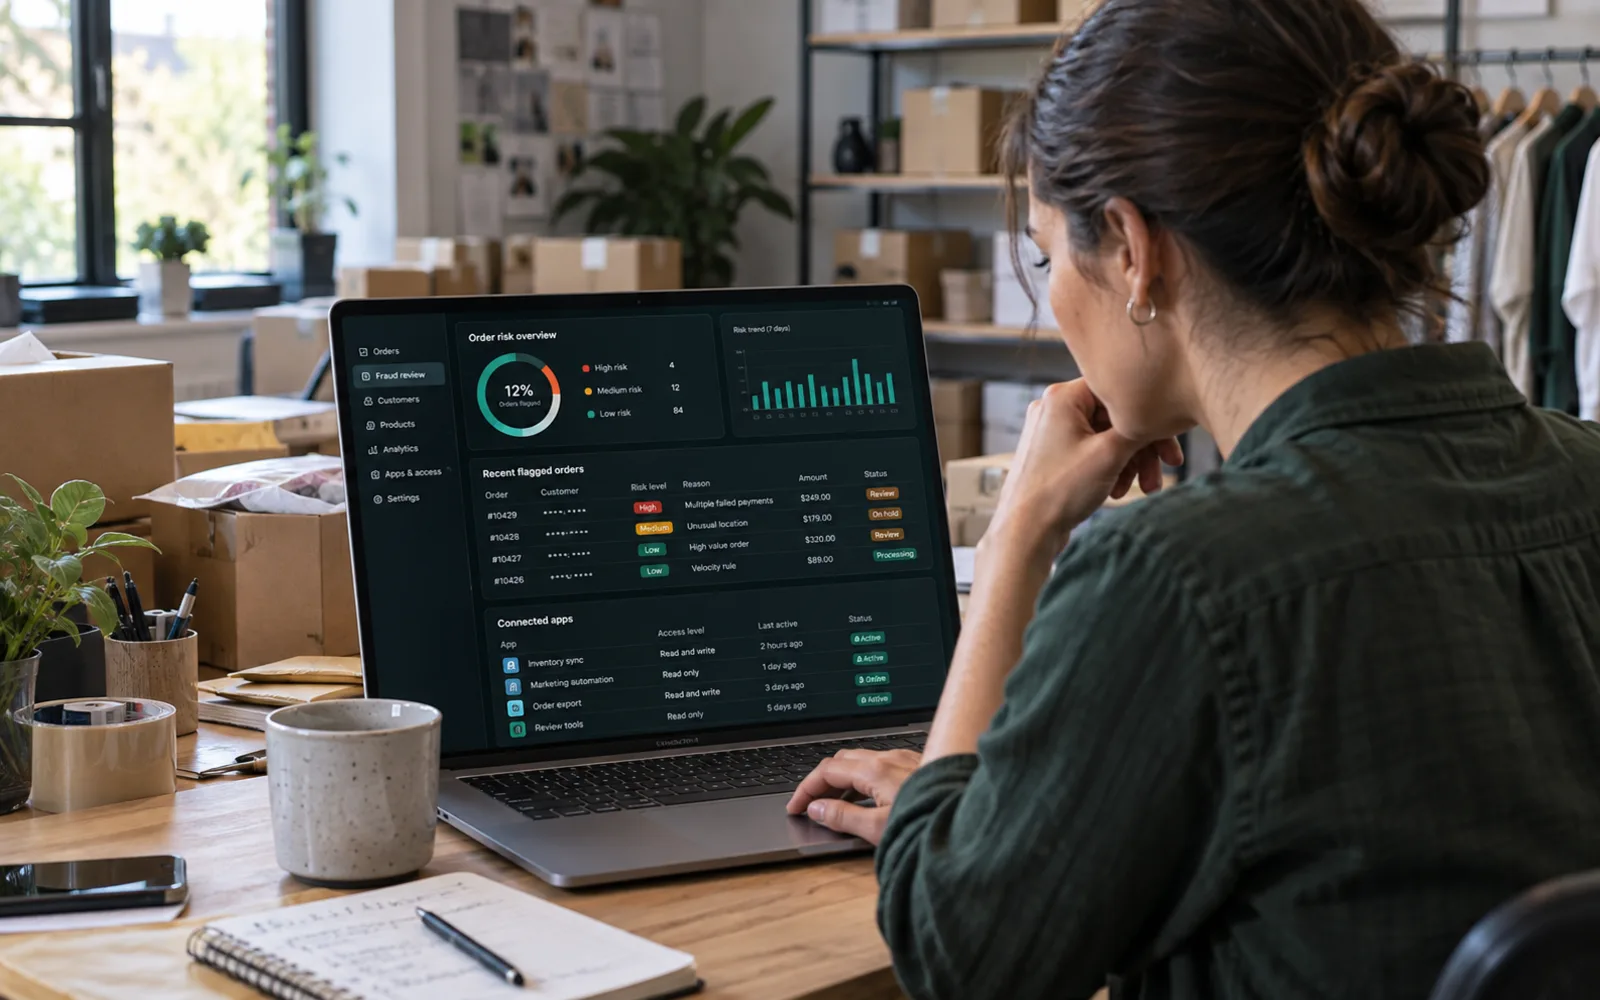
Get help with spam orders, suspicious activity and the security settings that matter to your Shopify store.

  • Bot and spam-order protection review
  • Suspicious-order workflows
  • Staff and connected-app access

Website security

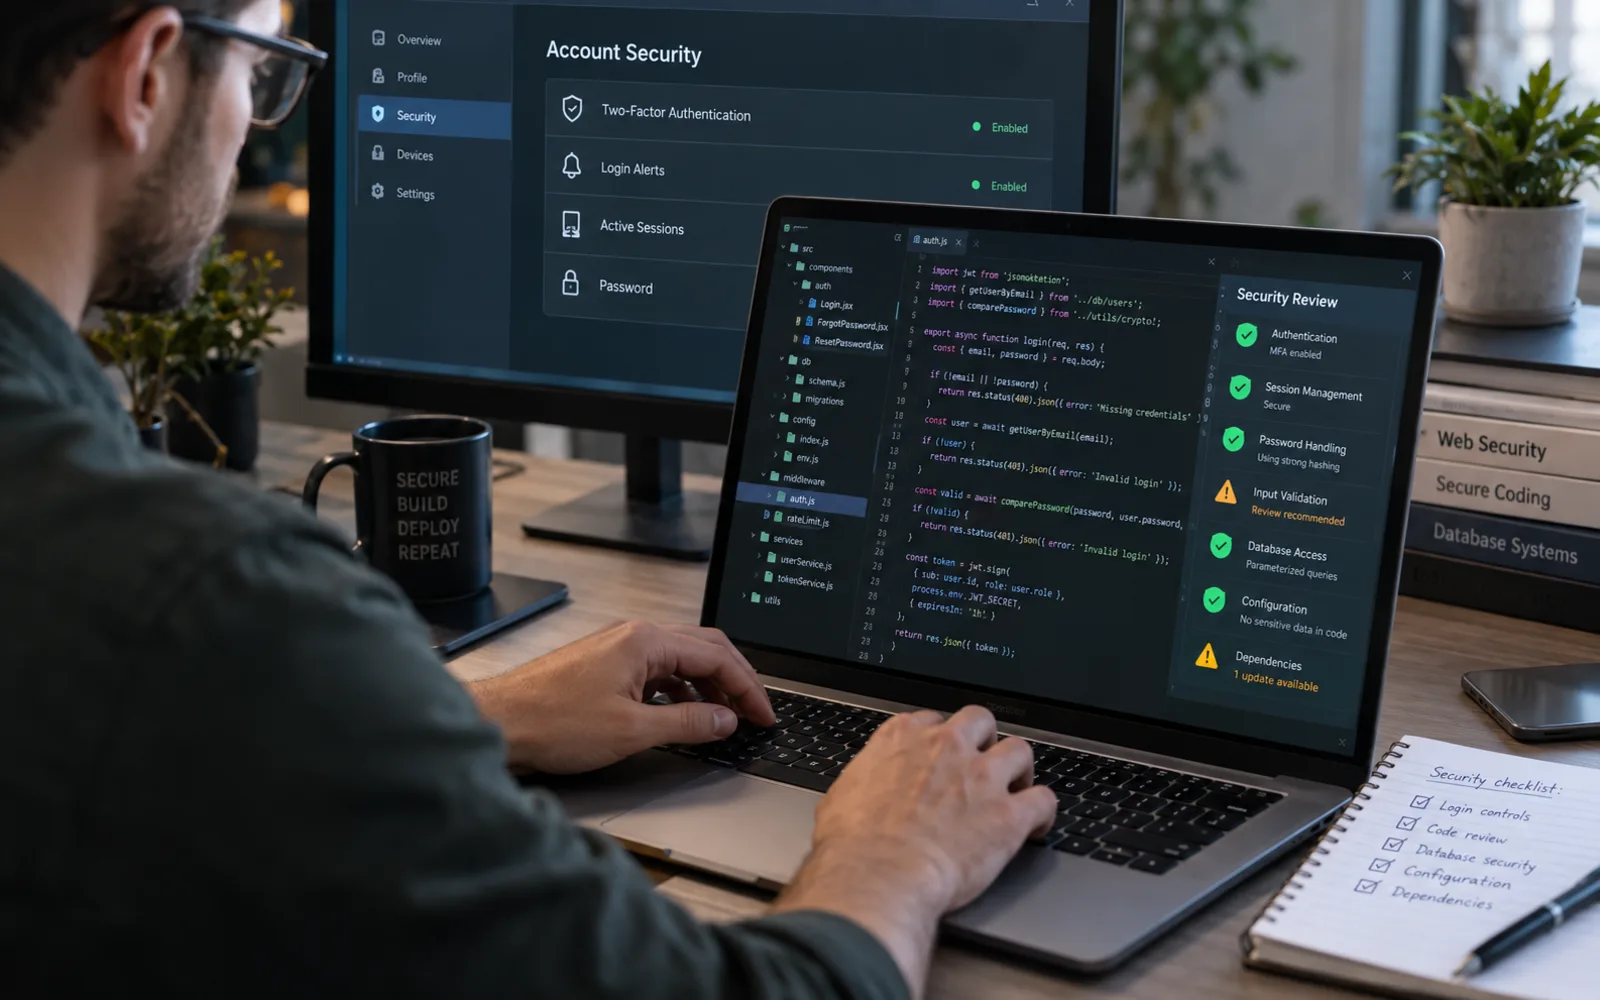
Practical reviews of login controls, database access and website settings for Laravel and custom websites.

  • Login and brute-force controls
  • Database security and secret handling
  • Dependencies and API access

Server security

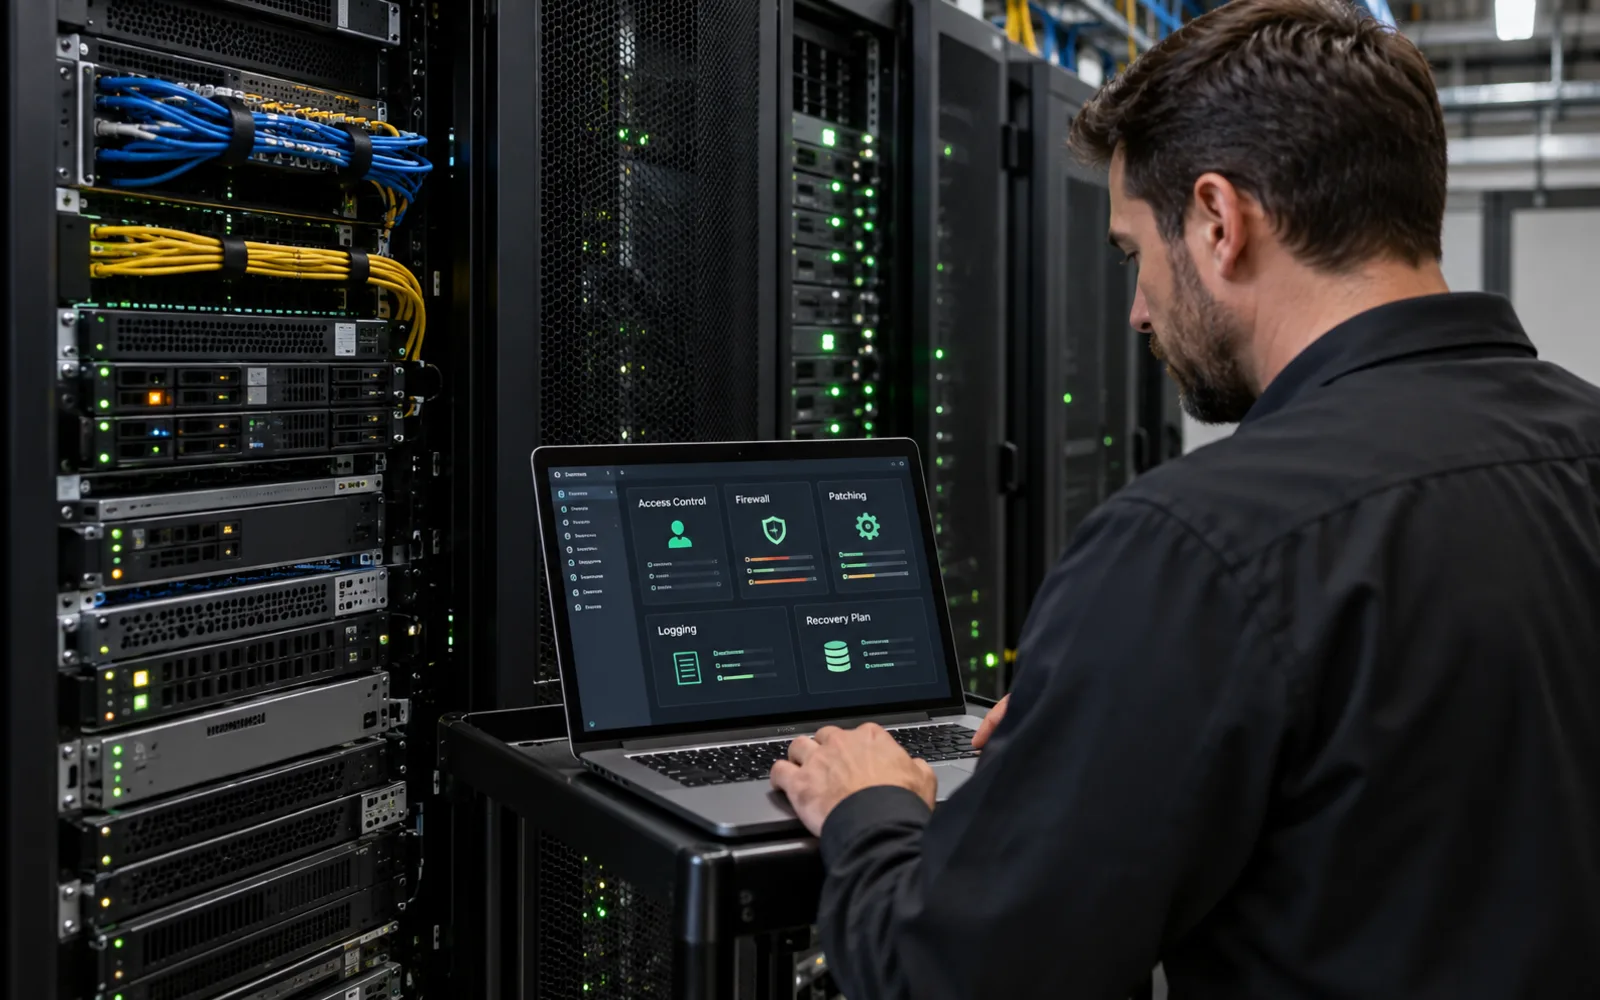
Understand exposed services, tighten access and plan the next steps for a more secure server.

  • Administrator access and firewall review
  • Patching and configuration
  • Logging and recovery planning

Company device security

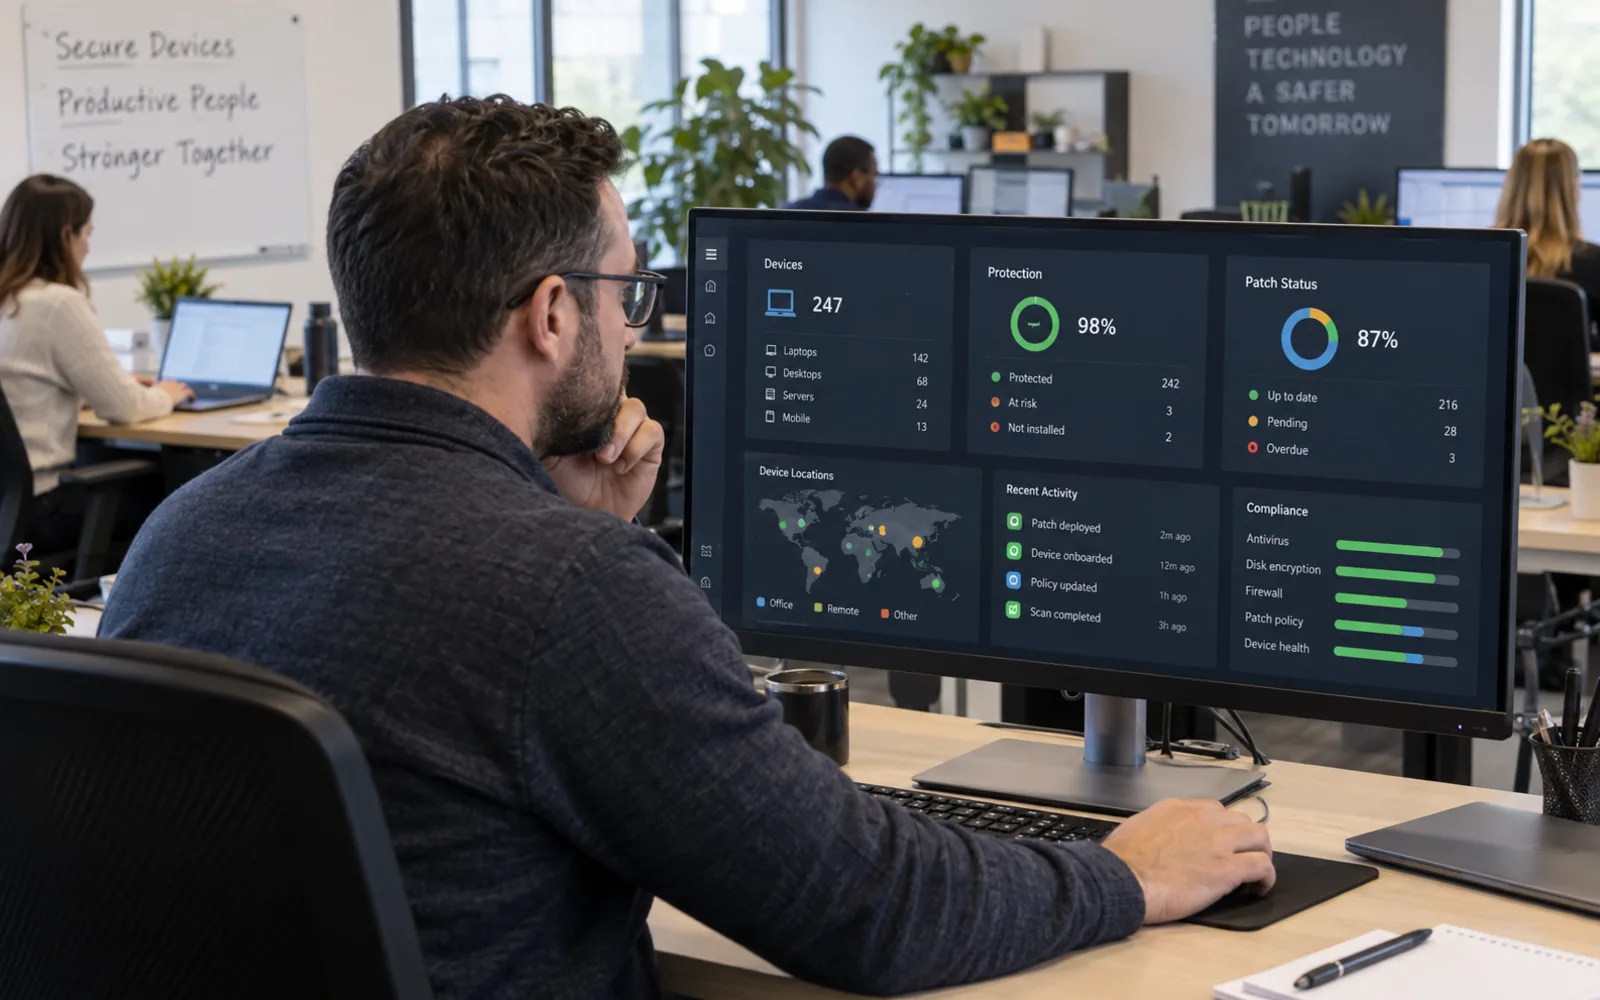
A clear device inventory, practical security recommendations and a scope that follows your actual device list.

  • Device inventory and baseline
  • Endpoint protection review
  • Patch policies and ongoing support
Assessment and operations

Security services

Independent assessment, tooling integration and recurring operational support for teams that need experienced help.

Security Integration

Design integrations so the signals that matter reach an owner who can act, with enough context to make a decision.

  • Tool landscape, interfaces and licensing
  • Signal design, enrichment and routing
  • Workflow, ownership and maintenance

Managed Security Services

Define a recurring service around the systems, controls and response responsibilities your business actually needs.

  • Coverage and responsibility boundaries
  • Review cadence, monitoring and escalation
  • Reporting, evidence and service review

Security Assessment

Scope an assessment that answers a specific question about your applications, infrastructure or data, and ends in prioritised actions.

  • Objectives, decisions and success criteria
  • Authorised scope, method and boundaries
  • Findings, prioritisation and next steps
WordPress sites

WordPress security

Login protection, firewall rules, activity logging and scanning for WordPress websites through the MaxMindSecurity Pro plugin, licensed from its own dashboard.

WordPress security

Login protection, site activity and monitoring, together in one dedicated workspace.

  • WordPress login protection
  • Updates and site activity
  • Website availability

WordPress Malware Removal

Get help investigating suspicious WordPress activity, removing malware where access allows, restoring safer files and planning hardening after cleanup.

  • Malware investigation and cleanup
  • Backup, restore and integrity review
  • Post-cleanup hardening and warnings
How work starts

A quote begins with the problem, then the service.

The first conversation is about what you run and what is worrying you. The service, the scope and the price follow from that, and all three are confirmed in writing before anything begins.

  1. 01

    Discover

    We review what you run, how traffic and data reach it, what controls exist today and the business concern behind the request.

  2. 02

    Scope

    We agree the systems in scope, the method, the deliverables, the responsibilities on each side and the commercial terms.

  3. 03

    Deliver

    We carry out the agreed work with clear updates, raising anything urgent as soon as it is found rather than saving it for a report.

  4. 04

    Improve

    You are left with prioritised findings, documented decisions and a named owner for each next step.

What every engagement includes

The parts that do not change, whichever service you choose.

01

A written scope

Systems, exclusions, method and responsibilities are documented before work starts, so there are no assumptions about who covers what.

02

Vendor-neutral advice

We work with the platforms you already hold. Where a change of tooling genuinely helps, we say why rather than assume it.

03

Findings tied to business risk

Recommendations are ordered by what is genuinely reachable and what it would cost you, not by raw severity counts.

04

A clear next step

Every engagement ends with prioritised actions and an owner for each, so the work continues after we hand over.

Common questions

Before you send an enquiry.

The questions we are asked most often about choosing a service, working with existing tools and how quotes are put together.

How do I know which service I need?

You do not have to decide before getting in touch. Most enquiries start with a symptom rather than a service name: unusual traffic, a failed customer security review, an upcoming launch or a cloud environment nobody has examined in a while. Describe the situation and we will confirm which service fits, or tell you if none does.

Can you work with the tools and providers we already use?

Usually, yes. Our services are scoped around your existing hosting, CDN, DNS, cloud platform, identity provider and security tooling. Share what you hold, including licence tiers, and we will confirm what is supported before proposing anything.

How does pricing work?

Every engagement is quoted after the requirements are reviewed. Scope, technology, effort, support hours and responsibilities are confirmed in a written proposal, so the price reflects the actual work rather than a package guess. There is no charge for the initial conversation.

Do you offer one-off projects or ongoing support?

Both. Many engagements are a scoped piece of work such as an assessment, a WAF rollout or a cloud review. Where recurring attention is needed, a managed arrangement defines what is covered, how often it is reviewed and how escalation works.

What happens after I request a quote?

We review the enquiry and come back to discuss scope. Nothing is deployed, tested or changed until the scope, authorisation and commercial terms are agreed in writing. Please do not send passwords, access keys or customer data with an initial enquiry.

Request a quote

Tell us what you need to protect.

Share the website, application, API, cloud environment or data concern behind the request. We review it and come back with a practical next step and a scoped proposal.

  • A reply by email from the person who will scope the work.
  • Scope, deliverables and price confirmed in writing before anything starts.
  • No account or payment is needed to send an enquiry.

Prefer email? Write to care@maxmindsecurity.com or use the contact page.

No account or payment needed. Please do not include passwords or access keys.