Server security
A stronger foundation for your server.
Understand exposed services, tighten access and plan the next steps for a more secure server.
Tell us what you run. We'll help define the next step.
What we focus on
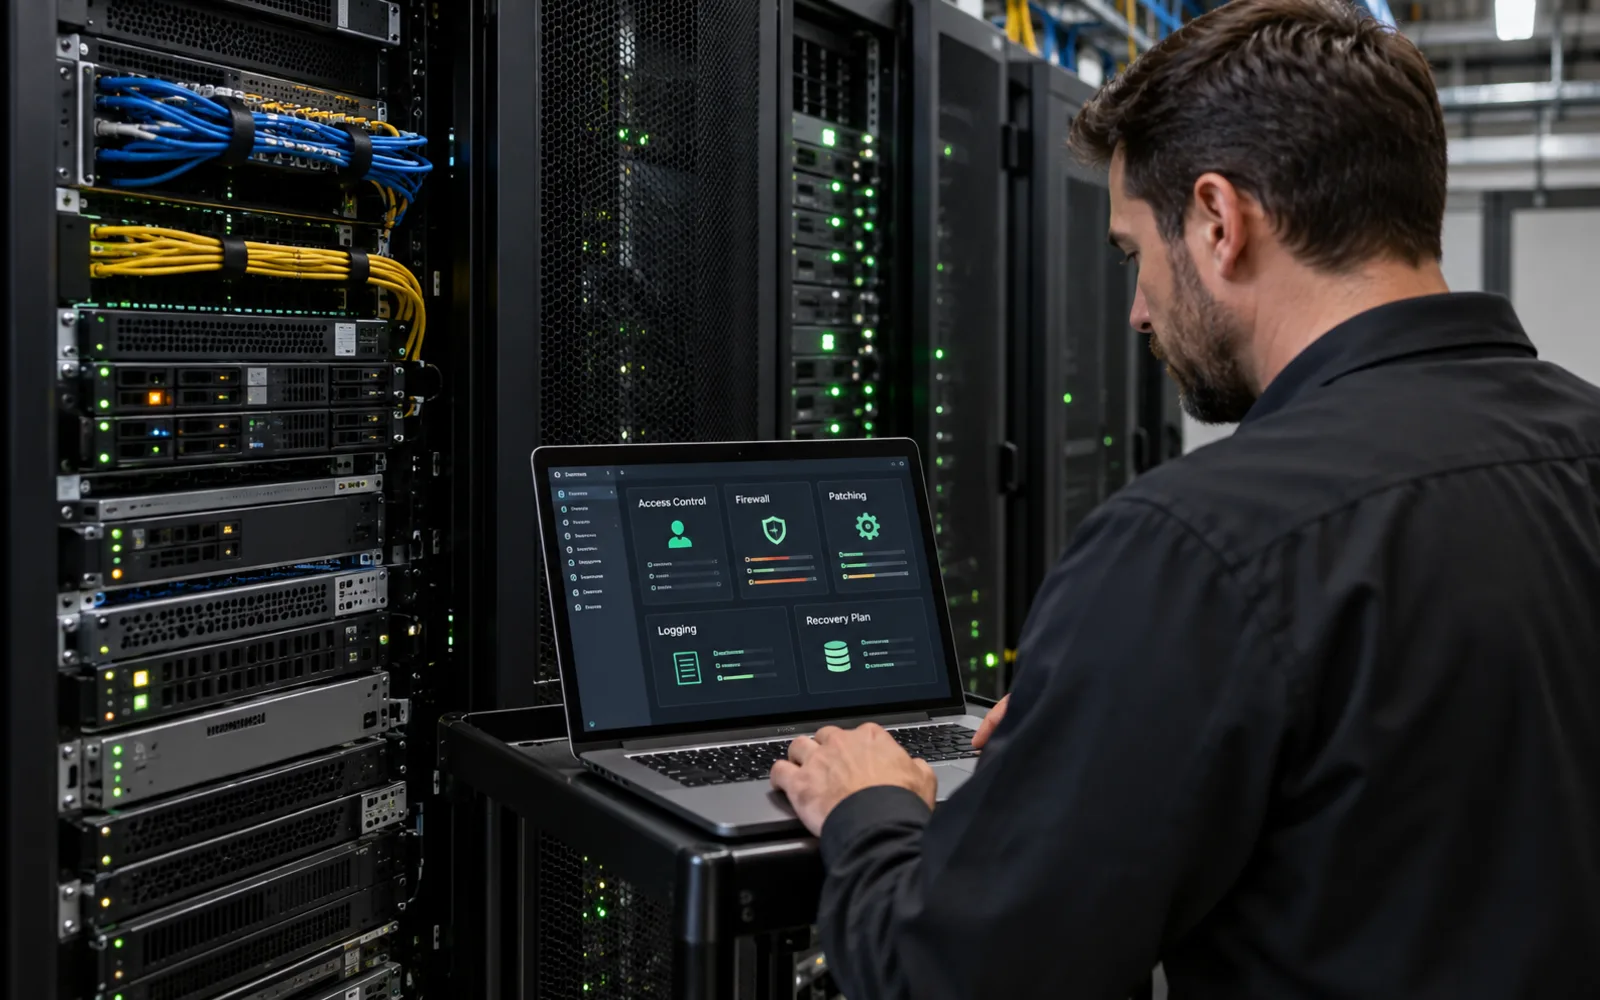
- Administrator access and firewall review
- Patching and configuration
- Logging and recovery planning
- Scoped to your environment
- Clear deliverables, agreed upfront
- No account needed to enquire
Server Security & Hardening Review
Build a more manageable security baseline for your server. Our server security services focus on administrator access, exposed services and configuration, with wider hardening and recovery planning included when the scope calls for it.
For businesses responsible for a VPS, cloud instance or dedicated server. Share the operating system, hosting provider and workload before setup. The access and changes available on a self-managed server differ from those on a managed or shared hosting plan.
Server security for access, exposure, patching and recovery
Self-managed servers give teams flexibility, but they also make security ownership very concrete. Administrator access, exposed services, firewall rules, patching, logging and backups all need clear decisions rather than assumptions.
MaxMindSecurity helps businesses review VPS, cloud instance and dedicated server security. The engagement can cover administrative access, SSH or remote access paths, firewall exposure, update recommendations, configuration hardening, logging policy and recovery planning.
The goal is not to produce a generic hardening checklist. A server running a production website, database, mail service, API or internal tool has different constraints. We identify what can be tightened safely and what needs a change window, provider coordination or application-owner approval.
Best fit for
- Businesses responsible for a VPS, cloud instance or dedicated server
- Teams unsure which ports, accounts or services are exposed
- Organisations that need patch, logging and recovery decisions documented
What you receive
- A clearer view of reachable services and administrator access
- Prioritized hardening and patch recommendations
- Practical logging, backup and recovery next steps
Server security areas we help you review
Server security starts with knowing who can administer the system, what is reachable from the network and how quickly the service can recover if something goes wrong.
Administrator and privileged access
We review administrator accounts, remote access methods, key handling, multi-factor options where available, sudo or privileged access and whether access still matches current responsibilities.
Network exposure and configuration
We examine reachable services, firewall rules, management ports, service configuration and provider-level controls. Recommendations are shaped around the workload so necessary traffic continues to work.
Patching, logging and recovery
We review update status, maintenance process, important logs, retention expectations, backup configuration and recovery responsibilities. A hardening plan is incomplete if nobody knows how to restore service after an incident.
A focused server security scope before hardening begins.
Before recommending changes, we confirm the operating system, workload, hosting provider, access model and tolerance for downtime.
Server role and constraints
We identify what the server runs, which users and services depend on it, and whether there are maintenance windows or provider constraints that affect hardening decisions.
Access and exposure review
We review how administrators connect, what is reachable from the internet or private networks, and whether firewall and provider controls match the intended service role.
Change plan and recovery
Recommendations separate quick wins from changes that need testing, maintenance windows or rollback plans. Backup and restore readiness are included so hardening does not ignore recovery.
Start with the right scope.
Tell us the operating system, the hosting provider and what the server runs. We agree what can be reviewed and changed safely, then send a written quote before anything is touched.
What a server security engagement can include
- Server role, workload and exposure summary
- Administrator and privileged-access review
- Firewall, reachable service and configuration review
- Patch and hardening recommendations
- Logging and evidence-retention guidance
- Backup and recovery readiness notes
- Quote-ready scope with technology, effort and responsibilities defined
Request a quote for server security
Share the systems involved, your priorities and the tools you already use. We reply by email with the scope, availability and pricing once we have reviewed what you send.
Your enquiry is with our team.
We will review what you sent and reply to your email address. Nothing starts until scope and price are agreed in writing.
Explore services in the meantimeA server review that balances security with uptime.
We move from exposure and access review to a practical change plan, so hardening supports the service instead of surprising it.
-
01
Server discovery
We confirm operating system, workload, provider controls, access model and business impact.
-
02
Exposure review
We review accounts, privileges, open services, firewall rules and configuration risk.
-
03
Hardening plan
We separate immediate recommendations from changes that need testing, coordination or maintenance windows.
-
04
Recovery handoff
We document logging, backup and restore recommendations alongside the hardening actions.
Questions teams ask before server hardening.
Server changes can affect uptime, access and application behavior. These answers explain how we keep the scope controlled.
Are all operating systems supported?
Support depends on your operating system, version, workload and access. Provide those details so we can confirm a suitable scope before service setup.
Does server hardening guarantee compliance?
No. A configuration review is not a compliance certification. If you need a specific benchmark or audit deliverable, discuss the requirements and evidence needed before agreeing the service.
How do I get started?
Send a quote request with the operating system and version, the hosting provider and the server's role. We reply by email to agree the scope, the access method and any maintenance windows before work begins.
How is server security work priced?
Each server is quoted after we understand its role, operating system and access model. The price reflects the written scope: an access and exposure review costs less than a review that also covers hardening changes, logging policy and recovery planning. Nothing is sold as a fixed plan.
Will patching cause downtime on our server?
It can, depending on the update and the workload running on the server. We account for application dependencies and agree suitable change windows before recommending or applying anything, and this is discussed as part of setup rather than assumed.
What happens if you find something urgent during the review?
We raise it as soon as it is found rather than saving it for a final report. Depending on severity and the access agreed, we recommend immediate steps you can take, and any remediation beyond the agreed scope is confirmed with you before proceeding.
Need a specific answer? Talk to our team
Further reading: Ubuntu infrastructure hardening guidance
Services that pair naturally with server security.
Servers often sit behind DNS, CDN, WAF and managed review processes. These services help cover the surrounding paths.