Traffic inspection
Review request paths, HTTP methods, headers, parameters, user agents and patterns that help distinguish normal visitors from suspicious web traffic.
Built around your application.
Deploy and tune a WAF to filter malicious HTTP traffic while keeping legitimate customers, integrations and business-critical journeys moving.
Tell us what you run. We'll help define the next step.
What we focus on
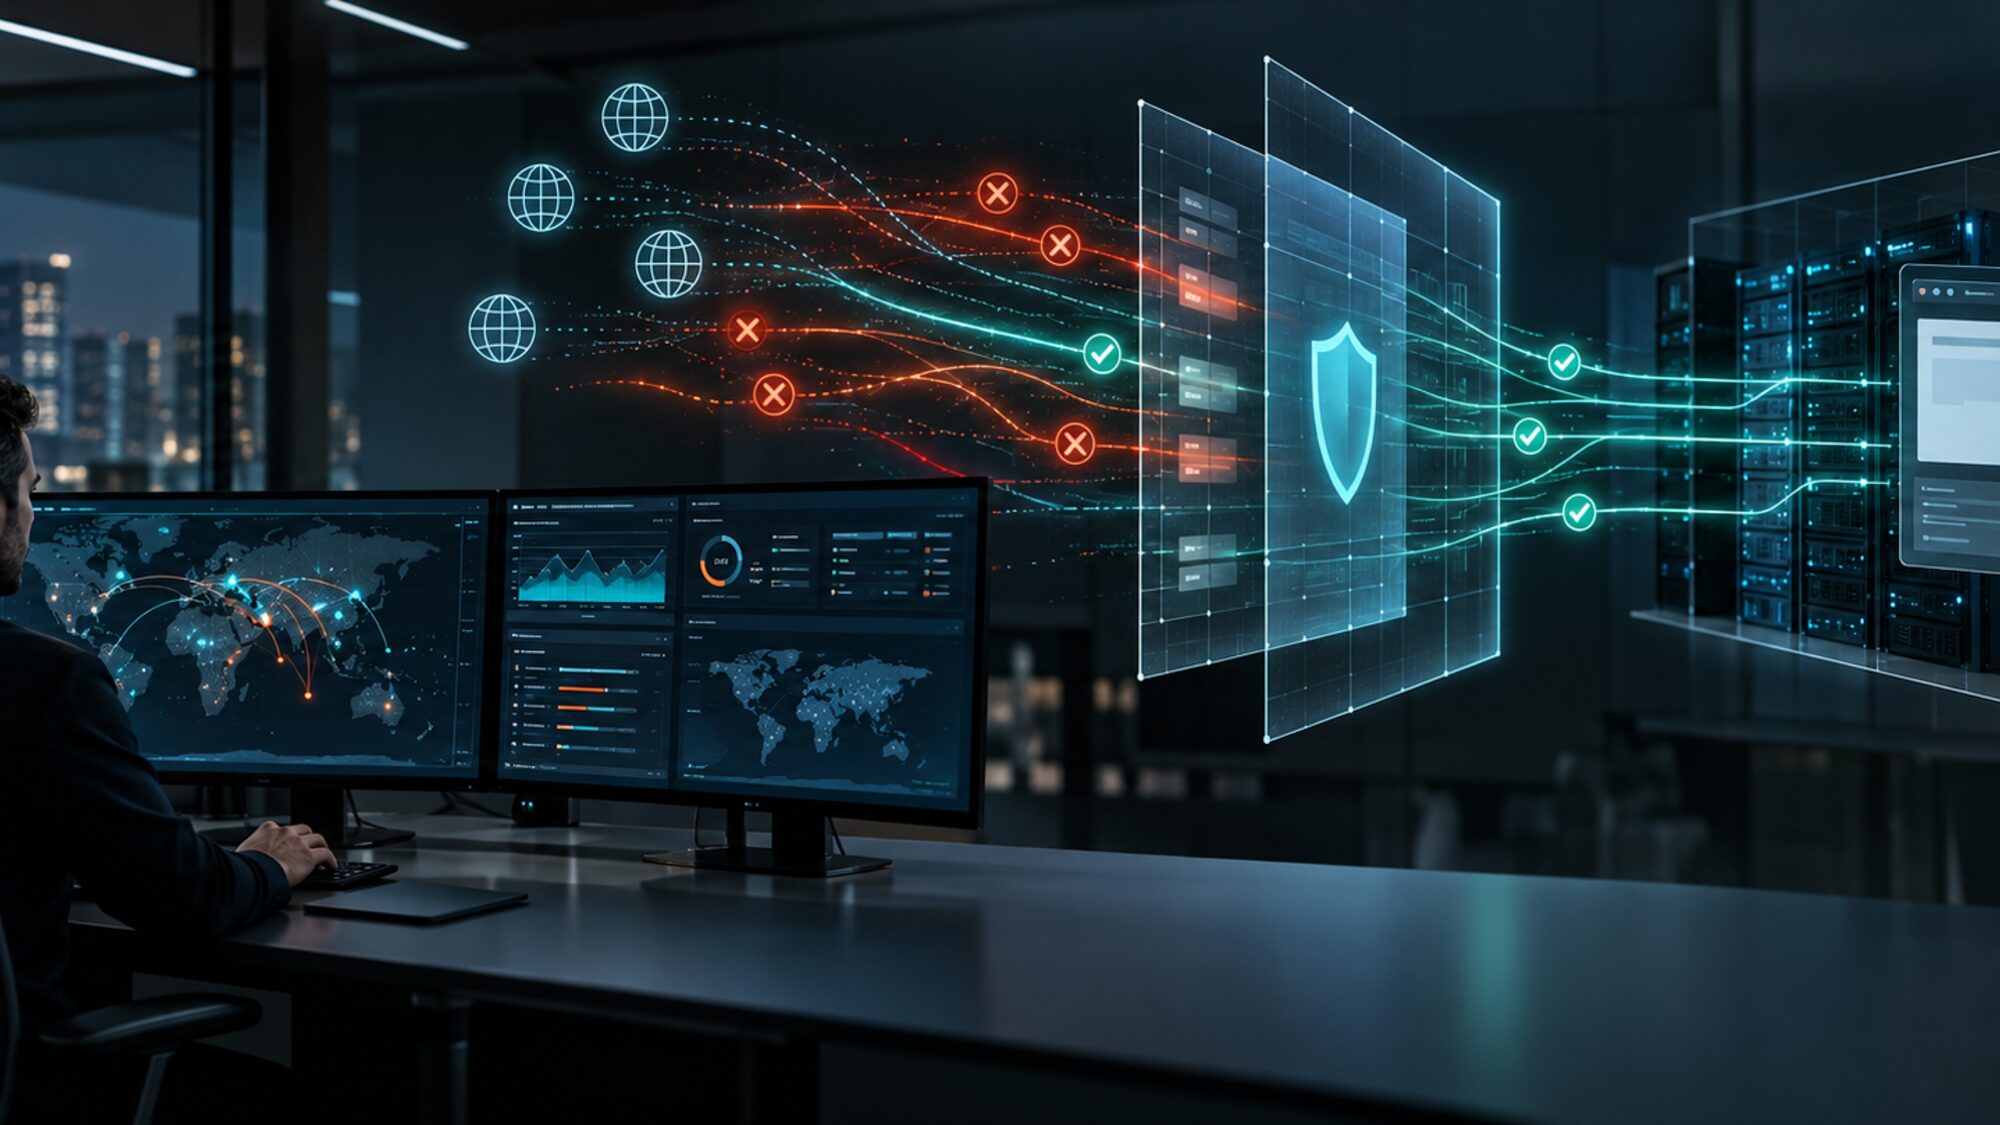
A web application firewall sits between internet traffic and your application, inspecting HTTP requests before they reach the origin. Generic managed rules provide a useful starting point, but effective protection depends on how your application works: its public hostnames, APIs, login flows, file uploads, third-party callbacks and release cycle.
Our WAF service is for organisations protecting customer-facing websites, portals, ecommerce journeys, SaaS products and APIs. We help teams choose a workable traffic path, reduce direct origin exposure, establish a rule baseline and introduce blocking controls in stages. The engagement is scoped around your current CDN, cloud platform, reverse proxy or WAF provider rather than forcing a particular vendor.
A Web Application Firewall service works best when it is shaped around the way your website or application behaves. We review public hostnames, origin access, login flows, forms, APIs, file uploads, admin panels and sensitive paths so WAF rules protect the application without blocking normal customers.
We plan the configuration, tune managed and custom rules, review the policy you already have and support the rollout on your CDN, cloud or reverse-proxy platform. The intent is to reduce common web attacks, automated probing and direct origin exposure at the application edge, and to say plainly where a WAF will not help, such as a business-logic flaw or a vulnerability that needs fixing in the code.
A good WAF implementation is not a switch you turn on and forget. It needs careful policy design, exception handling, monitoring, staged rollout and review of false positives. That is why this service focuses on practical deployment planning, rule behaviour and the operational process behind the firewall.
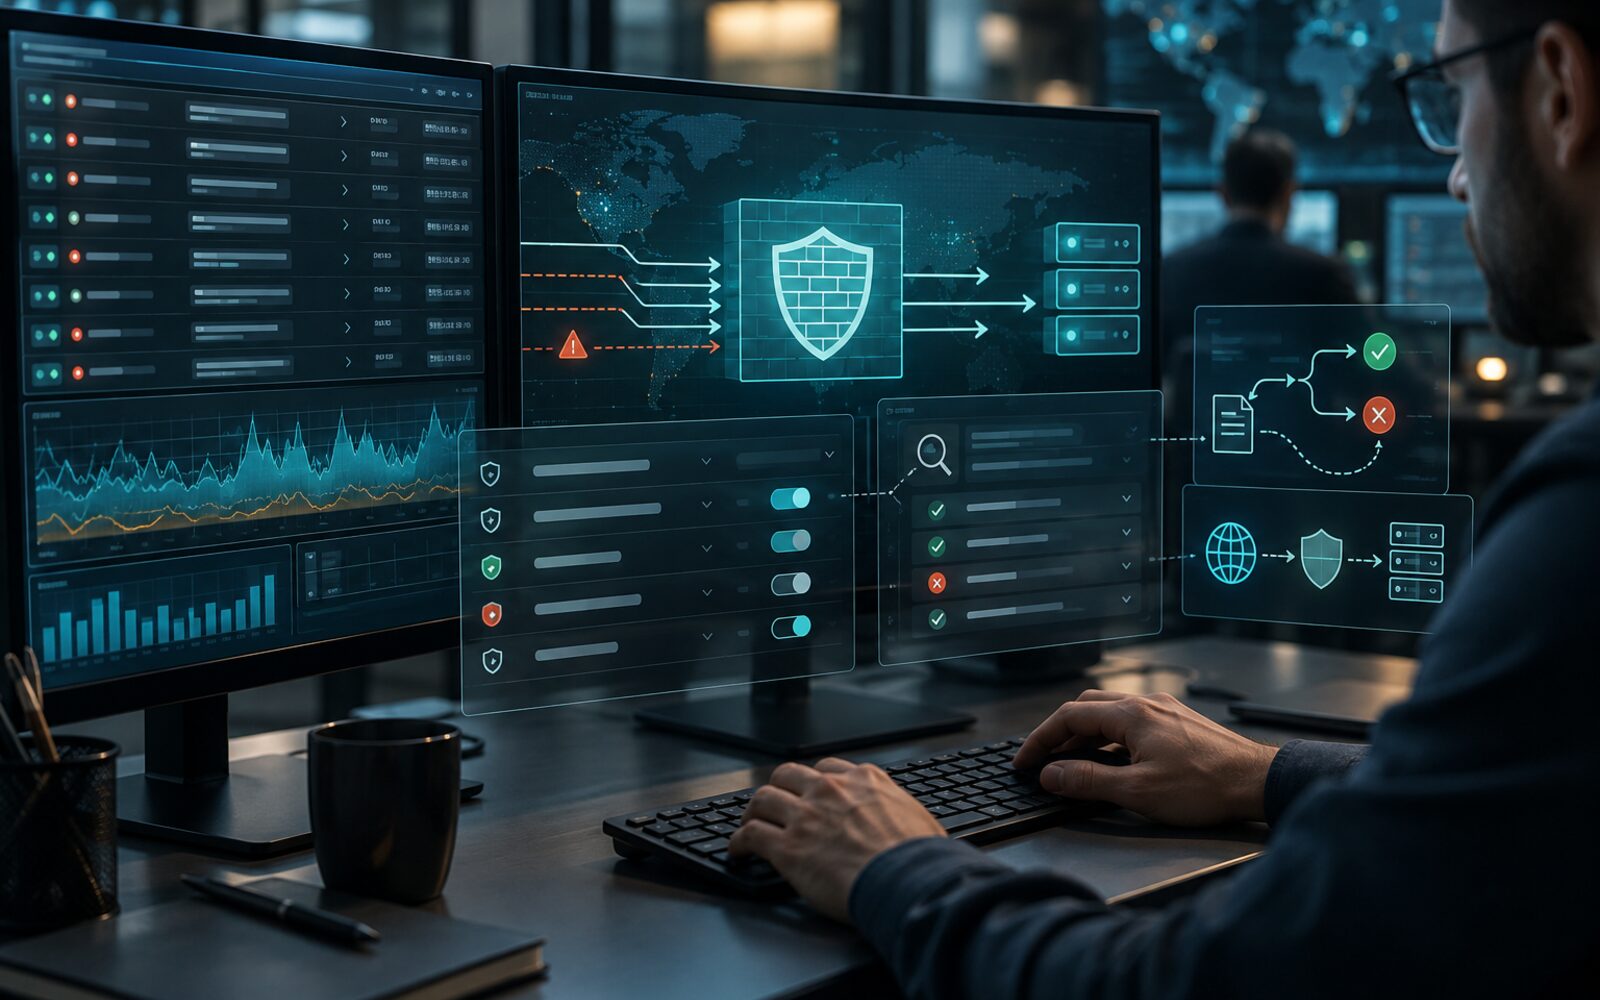
Review request paths, HTTP methods, headers, parameters, user agents and patterns that help distinguish normal visitors from suspicious web traffic.
Plan controls for common web attack classes such as the injection attempts listed in the OWASP Top 10, malicious payloads, scanner traffic, abusive requests and sensitive-path probing.
Reduce the chance that attackers can bypass the security edge and reach the application server directly.
Review managed rules, custom rules, exceptions, allow lists and block actions so protection fits the application.
Define how legitimate customer activity is tested, monitored and adjusted before aggressive blocking is enabled.
Plan who reviews alerts, how urgent events are handled and what evidence is needed for follow-up.
Map public hostnames, DNS, CDN or load balancer routes and the application origin. We review where inspection should occur and how direct access to the origin can be limited without interrupting administration, health checks or trusted integrations.
Review baseline managed rules, request-size limits, method restrictions, rate controls and exceptions against real application behaviour. Rules are prioritised around relevant web risks rather than enabled without context.
Define a monitor-first period, log review workflow and representative test cases before blocking is enabled. We agree change windows, exception ownership and rollback steps so the WAF can evolve with application releases.
Tell us which websites, applications or APIs you need to protect, how traffic reaches them today and which WAF, CDN or cloud tools you already use. We will confirm the proposed scope, platform responsibilities, deliverables, availability and pricing before work begins.
Share the systems involved, your priorities and the tools you already use. We reply by email with the scope, availability and pricing once we have reviewed what you send.
We will review what you sent and reply to your email address. Nothing starts until scope and price are agreed in writing.
Explore services in the meantimeWe review your environment, goals, current controls and the business concern behind the request.
We agree the systems, responsibilities, deliverables and commercial terms before work begins.
We carry out the agreed work with clear updates and practical evidence.
A firewall changes how every request reaches your application, so the questions are usually about coverage, false positives and downtime. These answers explain how we keep the rollout safe and measurable.
A WAF inspects HTTP traffic and can block or challenge requests that match configured attack or abuse patterns, including some of the injection and cross-site scripting attempts that the OWASP Top 10 ranks among the most common web application risks. Coverage depends on the policy and application, and a WAF cannot see or fix a logic flaw inside the application itself. A WAF complements secure development, patching, access control and monitoring; it does not replace them.
Often, yes. Share the provider, plan, application architecture and current configuration in your enquiry. We will confirm whether the technology is supported and whether the work covers review, tuning, migration or ongoing policy management.
We start with application context and observable traffic, then test the routes and actions most likely to be affected. Where an exception is necessary, the goal is to make it as narrow as practical by hostname, path, parameter, method or other supported condition rather than disabling a broad rule category.
A DNS or traffic-path change can introduce risk, so rollout planning includes prerequisites, validation, monitoring and rollback. Whether downtime is expected depends on your existing architecture, provider and change process; the proposal will state the agreed approach.
No. A CDN primarily distributes and caches content, while a network firewall controls traffic at network and transport layers. A WAF focuses on HTTP application traffic. Some platforms combine these capabilities, but each control still needs a clear role and configuration.
That depends on the engagement you agree. Some teams take the documented runbook and manage tuning and escalation themselves; others ask us to keep reviewing events, exceptions and rule changes under a managed arrangement. Either way, ownership for approving changes and handling incidents is defined before the WAF goes live.
Need a specific answer? Talk to our team
Further reading: OWASP Web Application Firewall overview