Company device security
Look after the devices your team relies on.
A clear device inventory, practical security recommendations and a scope that follows your actual device list.
Tell us what you run. We'll help define the next step.
What we focus on
- Device inventory and baseline
- Endpoint protection review
- Patch policies and ongoing support
- Scoped to your environment
- Clear deliverables, agreed upfront
- No account needed to enquire
Company Device & Endpoint Security
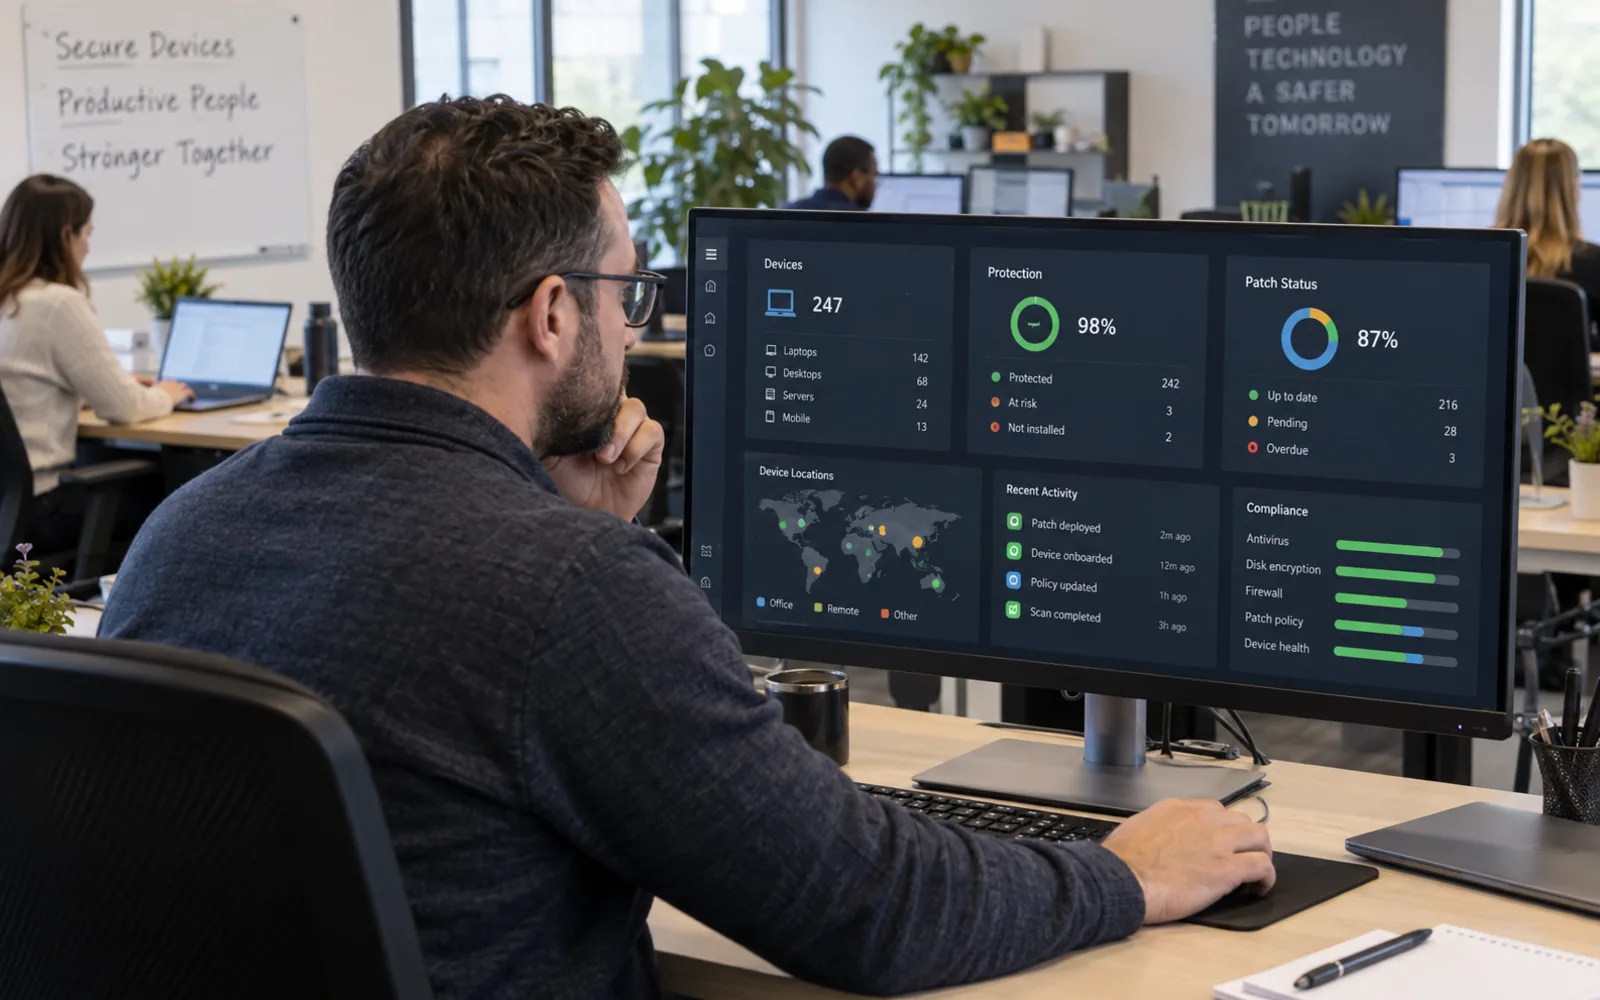
Keep a clearer picture of the computers your business relies on. Our company device security service combines device inventory, security baseline review and endpoint-policy recommendations, scoped to the computers you actually run.
For small businesses and growing companies managing office or remote-work computers. Device counts, operating systems and existing protection tools define the work, so count the computers you want included rather than estimating by employee count.
Company device security for inventory, endpoint controls and patch policy
Company devices are where business work happens: email, customer records, finance systems, admin portals, cloud dashboards and shared documents. Security becomes difficult when nobody has a current device list or a clear view of protection status.
MaxMindSecurity helps small businesses and growing teams review company computers, device inventory, endpoint protection, patch policies, encryption expectations and the reporting needed to keep follow-up work visible.
This service is not a promise to install a product on every machine immediately. It starts with a practical review of the devices in scope, what protection already exists and what changes can be coordinated with your IT provider or internal administrator.
Best fit for
- Small businesses managing office, hybrid or remote-work computers
- Teams that need a clearer device inventory and patch-policy review
- Companies unsure whether endpoint protection is configured consistently
What you receive
- A device inventory that can be assigned to owners
- Endpoint protection and patch-policy recommendations
- A monthly-summary model for tracking follow-up work
Company device security areas we help you review
Endpoint security is easier to improve when the device list, ownership, protection status and patch process are visible. We focus on practical controls a business can maintain.
Device inventory and ownership
We help establish which computers are in scope, who uses or owns each device, which operating system is running and whether remote or office devices need different handling. A useful inventory supports follow-up, not just counting hardware.
Endpoint protection and device baseline
We review existing endpoint protection, firewall status, disk encryption expectations, local administrator use and baseline settings where access allows. Recommendations are written around the tools and policies already in place.
Patch policy and reporting rhythm
We review how operating system and application updates are handled, how exceptions are tracked and what should appear in a monthly service summary. The goal is steady improvement without overwhelming the team.
A focused company device security scope before rollout decisions.
Before recommending tools or changes, we confirm device count, operating systems, existing controls, access model and who coordinates endpoint work.
Device count and operating model
We confirm how many devices are in scope, whether they are office, remote or hybrid, and who owns day-to-day administration. The scope and quote follow the actual device list.
Existing protection and policy
We review the endpoint tools, update process, encryption expectations and local administrator approach already in place. Where visibility is limited, that limitation is documented instead of hidden.
Recommendations and recurring review
Findings are turned into practical next steps and a reporting rhythm, so device security can improve over time instead of depending on one cleanup exercise.
Start with the right scope.
Tell us roughly how many computers you have, which operating systems they run and who looks after them today. We agree the scope with you and send a written quote before any review starts.
What a company device security engagement can include
- Company device inventory and ownership review
- Endpoint protection and baseline configuration review
- Patch-policy and update-process recommendations
- Local administrator and remote-work considerations
- Monthly company service summary structure
- Prioritized follow-up actions for IT or device owners
- Quote-ready scope with technology, effort and responsibilities defined
Request a quote for company device security
Share the systems involved, your priorities and the tools you already use. We reply by email with the scope, availability and pricing once we have reviewed what you send.
Your enquiry is with our team.
We will review what you sent and reply to your email address. Nothing starts until scope and price are agreed in writing.
Explore services in the meantimeA device review that creates visibility before rollout.
We move from inventory to practical policy recommendations, so device security becomes easier to maintain.
-
01
Device discovery
We confirm devices, owners, operating systems, locations and existing support arrangements.
-
02
Control review
We review endpoint protection, patch process, encryption, firewall status and administrator access where available.
-
03
Priority plan
We document which devices or policies need attention first and who should own each action.
-
04
Reporting rhythm
We define what should be tracked in a monthly summary so follow-up remains visible.
Questions teams ask before reviewing company devices.
Device security work affects real users, support teams and daily operations. These answers explain how we keep it practical.
Do you need access to every computer?
Not for the inventory and policy review. Much of it works from your existing device management console, your IT provider's records and a conversation with whoever administers the devices. Where a check needs direct access to a machine, we agree it with you first, and any device we could not verify is listed as such in the findings.
How do I get started?
Send a quote request with your approximate device count, the operating systems in use and who currently handles IT support. We reply by email to agree the scope before any review begins.
How many devices can be included?
There is no fixed package size. The scope and quote follow the device list you give us, whether that is a handful of laptops or several dozen office and remote computers. Tell us the approximate count and operating systems and we confirm the effort before work starts.
Will you install new endpoint protection software on our devices?
Not as part of the review itself. We review the endpoint protection and policies already in use and identify configuration questions and priorities. Any new protection product, licence or rollout is a separate decision, agreed with you before anything is installed.
What is included in the monthly company service summary?
Where your scope includes recurring review, the summary covers the recommendations from the inventory, endpoint protection and patch-policy review, along with anything that changed since the last summary, so you can coordinate next steps with your IT provider or internal administrator without digging through separate reports.
Can remote and office devices be mixed in the same scope?
Yes. The service is built around office or remote-work computers, so devices in different locations can be included in the same device list as long as you can provide the access needed for inventory and review.
Need a specific answer? Talk to our team
Further reading: Microsoft endpoint security overview
Services that pair naturally with company device security.
Device security often connects with managed support, security assessment and data security for the systems those devices reach.